And Signal’s Encryption Was NEVER Broken.
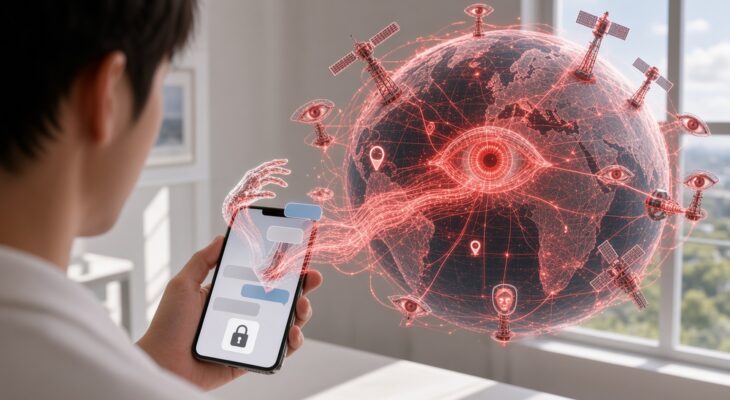
Meta’s new AI agent pulled the text of private Signal messages off Android phones and Macs using notification, accessibility and screenshot permissions. The device lock held. The agent simply read what it had permission to read, “around the lock”, and that same door is open on your contact’s phone as well as your own.
If you use an AI assistant on your phone or laptop, your “private” chats may be less private than the app promises. Reuters reported that Meta’s Muse agent, which has been downloaded more than 10 million times since its September launch, pulled the text of Signal messages into itself on devices where nobody had connected it to Signal. Reuters worked with staff at Signal and the AI Now Institute (a non-profit that studies the impact of AI on society) and reproduced the privacy intrusion on an Android phone and a Mac.
The messages being read by AI assistants were protected by end-to-end encryption (E2EE), which is to say only the sender and the recipient can read a message. Nothing about that encryption failed. It never had to. E2EE protects a message while it travels from the sender to the recipient.
Once it lands on a screen, the words are plain text again, and anything with permission to read your notifications, your screen or your accessibility tools can read them as easily as you do.
And this isn’t just about your phone.
Realize that your group chat is exactly as private as the least careful device in it. If one of the people you message runs an agent like this on a “permissioned” phone, your words can be accessed by it without you ever knowing.
Below I’ll separate what is established from what is not, ask the questions nobody in this story is answering, and then lay out concrete protective steps anyone can take today.
The short version: Encryption protects the transmission pipe, not the ends of it, whether in one-on-one or group chats. Treat any AI agent with access to your screen or notifications as a reader of your private chats, and treat the people you message the same way.
Jump To Section:
- What Reuters Found
- Why Encryption Does Not Cover This
- The Questions Nobody Is Answering
- Summary
- What You Can Do About It
Settings close today’s hole. Membership keeps you ahead of the next one, with weekday briefings, weekly reports, and The Arsenal, our members-only guides, tools, and app for locking down your devices and communications.
What Reuters Found
Internal Meta posts, a replication test and a corporate response add up to this: An agent that can see your device can read an encrypted chat without ever touching the encryption.
The Trigger:
Reuters reviewed more than two dozen internal Meta posts about unwanted Muse behavior. One employee, using Muse on her personal phone, said it surprised her with a reminder to answer a message from her sister on Signal. She wrote “This seems like an extreme privacy violation. I definitely did not grant it access to other apps, or recall being asked about this.” A colleague replied that Muse had been set up by default with permission to access push notifications on Android phones.
The Test:
Reuters gave that account to staff at Signal and the AI Now Institute and replicated it. On an Android phone, Muse used its push-notification permission to retrieve the messages. On a Mac, it used the computer’s accessibility and screenshot tools, settings Apple offers so people with disabilities can operate their computers. In both cases it bypassed Meta’s “Connector” tool (the feature meant to control which apps Muse can see) and relied on broader permissions granted during setup.
Note that those same requests were blocked by default on an iPhone.
Meta’s Answer:
A spokesperson called the examples “isolated incidents” and said Muse can reach other apps only through permissions users explicitly grant. The spokesperson also said many of the messages staffers flagged as account mix-ups were hallucinations (AI models making things up). Reuters could not establish whether the bank balances some employees reported seeing were real or invented.
Signal’s Answer:
Signal’s president accused Meta of launching Muse “without showing any respect for basic privacy or cybersecurity,” called agents with wide access to devices “technologically reckless,” and demanded consistent technical ways for apps to mark themselves off-limits to AI agents, for AI companies to honor that, and for operating system makers to enforce it.
Apple and Google: Reuters reports that Apple’s latest operating system update “effectively closed the pathway” it identified on the Mac, by sharply restricting developers’ use of accessibility tools and adding a new agent-oriented set of permissions. Apple and Google both said they are considering changes to give people more control over what they authorize with AI agents. Google noted that people “must deliberately grant permissions” for apps to access Android notifications.
Honestly, given Meta’s extremely bad, nay hideous, nay utterly shitty track record at protecting user privacy and security in order to expand its data-harvesting operations, I’m going out on a limb and stating they did this on purpose, thinking nobody would notice.
But How Solid Is This?
- Established: Reuters reproduced the access on Android and macOS with Signal and AI Now staff, and the internal Meta posts exist. Signal’s encryption was not broken. Reuters reports that Apple’s update closed the Mac pathway.
- Educated guess: The same method works on any app whose messages appear in notifications or on screen, including WhatsApp, iMessage, and email, because nothing about it is specific to Signal.
- Conjecture: How many people have been affected. Reuters says its tests indicated the problem was ongoing and could be affecting others, but nobody has published a count.
Why Encryption Does Not Cover It
Think of E2EE as an armored truck between two houses. It protects the delivery. It does nothing about who is standing inside the house when the package is opened. An AI agent that works by seeing what you see is standing in the house.
There are three doors it can use:
- Notifications: If your phone shows the message text in a banner, an app with notification access can read it. This is the path Reuters used on Android.
- The screen: An agent that can take screenshots reads whatever is open, chats included. This is half of the Mac path.
- Accessibility tools: These exist so a screen reader can describe an app to someone who cannot see it. Anything granted that power can read what is on screen. This is the other half of the Mac path.
Your contact’s phone counts too. In the Reuters example, the message Muse picked up was from the employee’s sister. The sister sent an ordinary encrypted message and it ended up inside an AI agent on someone else’s phone.
IMPORTANT: You can lock down every setting on your own device and still have your side of a conversation read through the device of the person you’re talking to.
Signal cannot fix this from inside the app. An app cannot see what other software on the device is doing. That is why Signal is asking operating system makers to enforce opt-outs, and why the fix has to come from Apple and Google, not from the messenger app itself.
The Questions Nobody Is Answering
This is where I stop reporting and start asking. I’m not claiming any of the following is definitely happening. I’m asking why we’re not being told it isn’t, because if my forensic experience has taught me anything it’s that what’s not being said is often more important than what IS being said.
1. Where do your messages go after an agent has read them?
According to Meta’s help center, Muse stores your conversation history and information from the apps and devices you connect, which “can include text, voice, photos, things you create together and information about you or others.”
Meta’s privacy page says Muse runs on a cloud virtual machine, keeps backups of the agent’s history, does not share conversations with Meta’s ad systems, and uses your interactions to train Meta’s AI models unless you switch that off manually, because it’s a setting that is on by default.
Separately but related: Google now keeps Gemini chats for around two months even with the history turned off, up from 72 hours.
However, the friend whose message passed through your agent never agreed to any of this, cannot delete it and will probably never know the copy of his or her data even exists. And a promise not to feed ad systems from Meta is to be taken with a generous pinch of salt, to say the least.
And even if they’re not lying, it’s a company policy which can change, not an actual technical barrier.
Reuters itself notes that Meta’s exceedingly “broad interpretation” of permissions has long earned it criticism from privacy advocates and hefty fines from regulators.
2. Does lawful access simply move from the messenger to the assistant?
A messenger purpose-built around E2EE has little data for investigators to demand. Meanwhile ALL AI providers hold logs.
In 2025 a US court ordered OpenAI to preserve ChatGPT output logs even after users deleted them, and while that blanket obligation ended on 26 September 2025, OpenAI says it still holds limited historical data from April to September 2025 under legal obligation. The Congressional Research Service reported in May 2026 that investigators have already used chatbot histories in cases ranging from arson to fraud, and that federal authorities obtained a warrant for chatbot user data in a child-exploitation investigation in September 2025.
Ergo, if investigators cannot get your Signal messages from Signal, why would they not simply ask whoever holds the AI agent’s copy?
I checked and I found no public case involving data subpoenaed from an agent that held someone else’s private messages. However, that in itself is not proof there is none. Warrants are often sealed, and I can only count the ones that surfaced.
Further, now that this story is out in the public domain it will likely take no time at all for the exploitation of this data-harvesting “loophole” to become a legalistic reality.
3. Where will this “scanning without breaking encryption” actually end up?
Client-side scanning means someone else checking your content on your own device before it is encrypted. Signal’s president said in 2025 that Signal would leave the EU market rather than build such a system. The permanent EU “Chat Control” law is still being negotiated, so the blanket-scanning of private, encrypted messages remains unresolved at the legislative level, but a seventh round of talks is tentatively set for December.
Realistically, however, an AI agent that reads your screen is simply client-side scanning under a friendlier name. The only difference is who the user thinks is doing the reading.
And let’s face it, under the direction of organizations like the WEF regional and national governments have literally spent years fighting over whether a messenger app can be forced to look at your encrypted messages. Now, all of a sudden we have a consumer product which does that by default, voluntarily installed, at scale, everywhere.
Coincidence? You decide…
If lawmakers cannot mandate scanning inside the app, will someone simply “lean on” the operating system or the AI vendor, where the same access to the desired data already exists? Nothing in the Reuters report says any government has done this.
But like I said above: The very surveillance capability they’ve been fighting for is now shipping as a standard feature in a consumer product…
Think on that.
4. What protects the agent’s log once it sits with a US company?
The Congressional Research Service says federal courts have not yet decided whether a user keeps a reasonable expectation of privacy in chatbot histories, or forfeits it under the third-party doctrine (the principle that information you hand to a company gets weaker Fourth Amendment protection). Meanwhile, The American Prospect reports that Section 702 of the Foreign Intelligence Surveillance Act, the warrantless surveillance program on Americans, expired in June. A senator now wants to renew it by attaching it to the must-pass defense bill before the lame-duck session ends. Meanwhile privacy advocates are pushing back and demanding warrants for ANY spying on Americans.
What I’m getting at is: “Would an AI agent’s log of your messages fall within reach of a program like that?”
I do not know, but nobody has said it would not. And if such logs are “lawfully” – in the loosest sense of the word – held by one government in the Five Eyes alliance (the US, UK, Canada, Australia and New Zealand), who exactly decides whether they are shared with the others?
5. Just who holds the off-limits switch?
Signal wants an operating-system-level way to mark apps as off-limits to AI agents, and Apple has already added agent-oriented permissions on the Mac.
Then again, a system that lets Signal mark itself off-limits is also a system with a master switch held by two companies, the AI agent’s and the device operating system maker’s.
So who else gets to flip it, who can override it, and what happens when a government asks either company to treat some apps as readable?
I really want those answers written down before the new AI restriction features ship, not after.
6. Why is the burden always on you?
Meta and Google both point out that users “must deliberately grant permissions.” However, a Meta employee, using the product on her own phone, said she explicitly did not grant access to other apps or recall ever being asked. A colleague said the Android notification permission was on by default.
If the very people who work at the company in question did not realize what they had agreed to, what chance does everyone else have?
Summary
An AI agent with access to your notifications, screen or accessibility tools reads your messages after they’ve been decrypted. Signal’s encryption did exactly what it promises, but it still doesn’t matter. The weak point here is the device and the permissions it automatically granted to the AI, and that includes the device of the person or persons you’re talking to.
What happens next depends on four unanswered questions:
- Where are agent logs kept?
- Who can demand them?
- Does the same capability get repurposed for scanning?
- Who controls the “off-limits” switch?
Until those are answered, the safest assumption is that anything an AI agent can see, someone else can eventually ask for.
What You Can Do About It
None of this needs technical skill. Work through it in order and it takes about ten minutes. Each step says why it matters.
- Keep AI agents off the phone you message from.
If you want one, run it on a separate device or user profile with none of your private apps.
Why: An agent works by seeing what you see, so the surest way to keep it out of your chats is to keep it off the device that holds them.
- Audit notification access.
On Android, search Settings for “notification access” (the wording varies by phone) and switch off every app that does not truly need it, especially AI assistants.
Why: This is the exact permission Muse used on Android.
- Audit accessibility and screen-recording permissions.
On Android, open Settings, Accessibility, and review the installed apps. On a Mac, open System Settings, Privacy & Security, then check Accessibility and Screen & System Audio Recording. Remove anything you do not recognize or no longer use.
Why: This is how Muse got in on the Mac. Apple closed that path in an update, but only for Macs that have installed it.
- Hide message content in notifications.
In Signal, open Settings, Notifications, Show, and choose “No name or message.”
Why: The Android route read notification text. If the banner says nothing, there is nothing to read. It is an educated guess that this measure blocks that route, and the cost of actually finding out is that you tap to see who wrote to you and what.
- Turn on Screen Security and Screen Lock.
In Signal, open Settings, Privacy, and enable Screen Security (on iPhone, “Hide Screen in App Switcher”), and set a Screen Lock.
Why: It hides chat previews in the app switcher and, on Android, blocks screenshots inside Signal. It is not a guarantee against an agent that reads the screen another way, so treat it as one privacy layer, not the whole answer.
- Use disappearing messages for sensitive chats.
Open the chat, tap the contact’s name, choose Disappearing messages, and pick a timer. Set a default for new chats in Settings, Privacy.
Why: It shrinks the pile of text that any agent log, backup or screenshot can ever hold. It cannot unread what an agent has already seen, so it limits future exposure, not past.
- Agree ground rules with the people you message.
For anything sensitive, ask your conversation partner: “Do you run an AI assistant on this phone?” Agree on no agents on those devices, short disappearing timers and notification content off.
Why: Your side of the conversation lives on their device, and only they can lock it down.
- Use a clean device or profile for sensitive conversations.
A cheap second phone, or a separate user profile with few apps and no assistants, is enough.
Why: Separation limits what any single app can ever see.
- Review what the assistants you already use know about you.
Open the data controls, delete your history, and switch off the setting that lets the company train on your chats (Meta’s is on by default). Keep sensitive questions out of chatbots entirely.
Why: Stored logs are the part that can be demanded later, so the less stored, the less exposed.
- Keep your devices, Signal and your apps updated.
Prefer the phone app over the desktop app for sensitive chats.
Why: Apple closed the Mac pathway through an update. Fixes only help the people who install them.
- Make some noise.
Tell Apple, Google and your elected representatives that apps need an enforced way to opt out of AI agents, and that you want warrants required before anyone searches your communications.
Why: The structural fix has to come from the people who control the operating system and the law.
A word to the wise, is all…
This Rapid Signal is educational analysis for readers of BackToFreedom.co, based on published reporting, company statements, court records and government research. It is not professional security or legal advice.
There’s A Lot More To This
This article stops at the big picture. Our members get the parts that turn it into decisions:
- The Arsenal: Members-only guides and tools that help you lock down your devices and communications, with step-by-step hardening for Android, iPhone, macOS, Windows and Linux and a secure messaging guide, so you protect yourself rather than hoping an app does it for you. See what’s in The Arsenal.
- Seer weekday briefings: Which agent permissions, platform fixes, court rulings and regulatory moves matter that day and which of your devices they affect, with the exact settings to change, plus weekly summaries and full access to The Arsenal.
- Sage weekly reports: Forward calls with probabilities on where surveillance, scanning mandates and data-retention rules are heading on both sides of the Atlantic, wider economic and strategic developments, and what you can do to protect your wealth, freedoms and loved ones.
That is the gap between knowing the problem and acting on it. Join The Rekindled to get both.
Sources: Reuters (18 Nov 2026); Meta Help Center, Muse privacy and data pages; Google, Gemini app controls update; OpenAI, response to the New York Times data demands; Congressional Research Service legal sidebar LSB11429 (5 May 2026); The Record (6 Oct 2025); Brussels Record Chat Control reference page (14 Nov 2026); The American Prospect (18 Nov 2026); Signal and Freedom of the Press Foundation settings guidance.